Why Enterprises Trust OIA Shield24
Discover the full suite of security, governance, and zero-trust routing capabilities engineered natively into OIA Shield24.
Zero-Trust Token Encryption
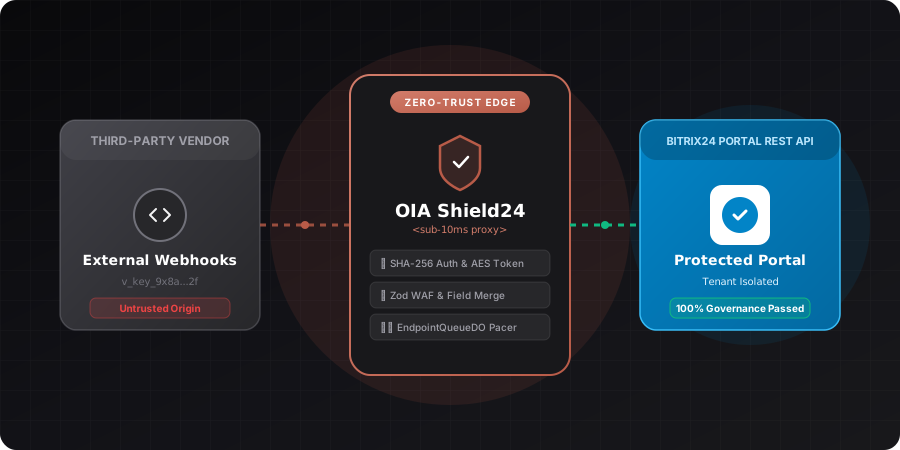
OIA Shield24 stores proxy keys strictly as SHA-256 hashes. Bitrix24 OAuth tokens are encrypted symmetrically via AES-GCM and refreshed on-the-fly without exposing credentials.
Precision Payload Forcing
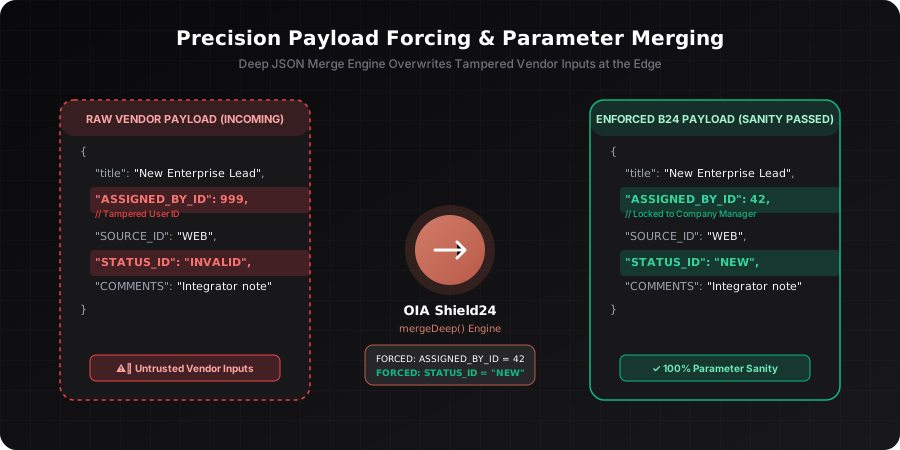
OIA Shield24 performs deep JSON merges to automatically inject static fields (e.g. ASSIGNED_BY_ID, fixed status codes) into vendor requests, blocking parameter tampering.
Durable Rate Pacing
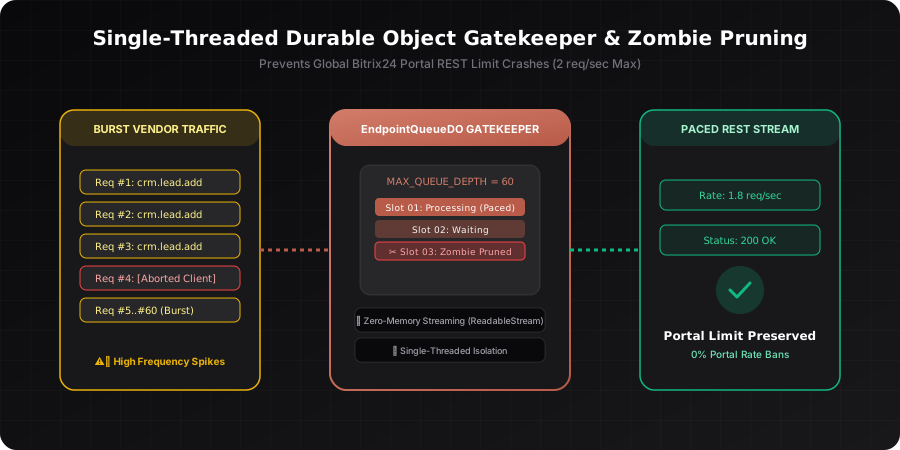
OIA Shield24 spins up single-threaded Durable Object queues per endpoint to enforce soft RPM throttling, featuring Zombie Request Pruning to protect global Bitrix24 limits.
Method & Scope Sandboxing
OIA Shield24 restricts vendors strictly to explicitly allowed Bitrix24 REST methods (e.g. crm.lead.add) and enforces allowed HTTP verbs (GET, POST, PUT, DELETE).
CIDR IP & CORS Shield
Block rogue traffic at the edge. OIA Shield24 filters caller IPs against CIDR network allowlists and enforces origin domain restrictions before traffic touches Bitrix24.
Multi-Region Data Residency
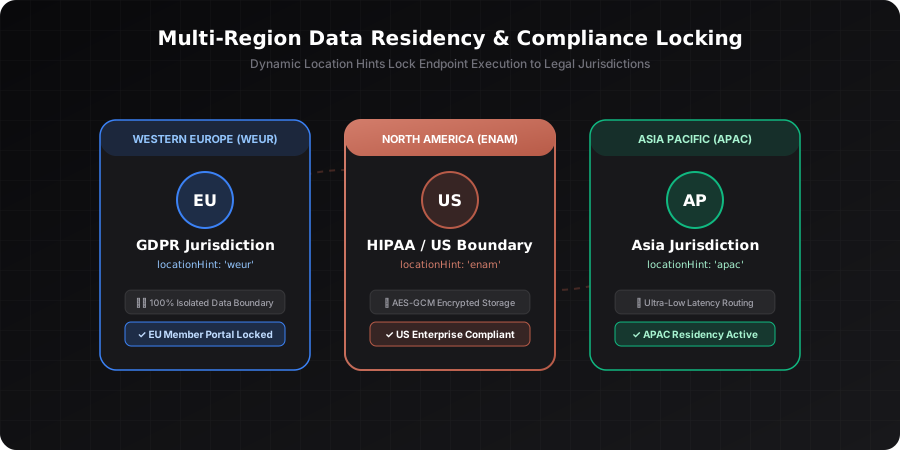
OIA Shield24 binds vendor endpoints strictly to Western Europe (weur), North America (enam), or Asia to satisfy GDPR, HIPAA, and regional laws.
Member ID Alias Masking
OIA Shield24 masks your Bitrix24 portal Member ID using cryptographic alias routing, so a vendor's webhook URL never reveals your internal portal identity.
Outbound Event Router
OIA Shield24 multiplexes Bitrix24 events to multiple external webhooks with exponential backoff retries via regional OutboundEventDO engines.