OIA Shield24
Install On Bitrix24
Bitrix24 Marketplace Official Partner

Protect Your Bitrix24 Portal
with OIA Shield24.

OIA Shield24 is the master enterprise API gateway and zero-trust proxy built specifically for Bitrix24. Eliminate unmonitored vendor webhooks, enforce field-level payload security, and maintain 100% tenant isolation at the edge.

Install On Bitrix24 Explore Core Features
Core Platform Capabilities

Why Enterprises Trust OIA Shield24

Discover the full suite of security, governance, and zero-trust routing capabilities engineered natively into OIA Shield24.

01

Zero-Trust Token Encryption

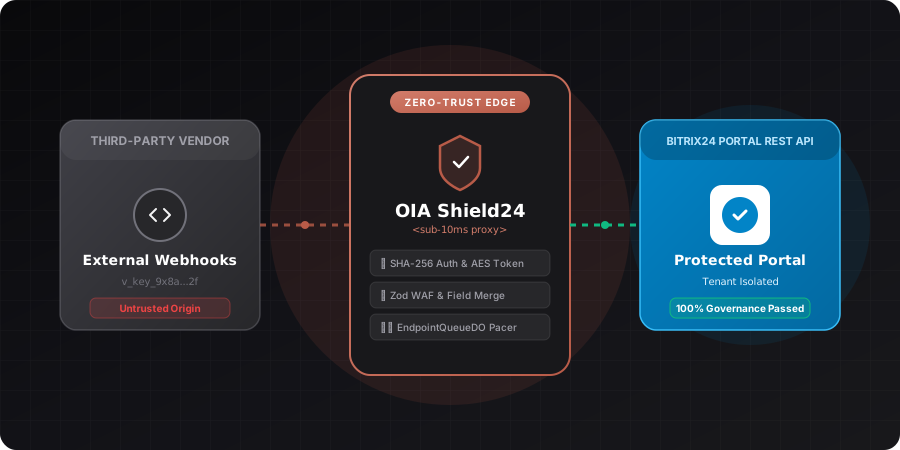
OIA Shield24 stores proxy keys strictly as SHA-256 hashes. Bitrix24 OAuth tokens are encrypted symmetrically via AES-GCM and refreshed on-the-fly without exposing credentials.

AES-GCM Web Crypto
02

Precision Payload Forcing

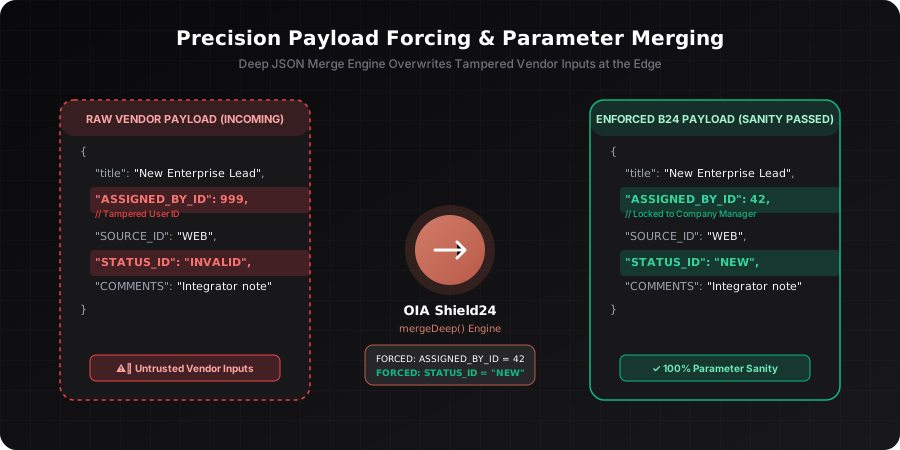
OIA Shield24 performs deep JSON merges to automatically inject static fields (e.g. ASSIGNED_BY_ID, fixed status codes) into vendor requests, blocking parameter tampering.

Deep JSON Override
03

Durable Rate Pacing

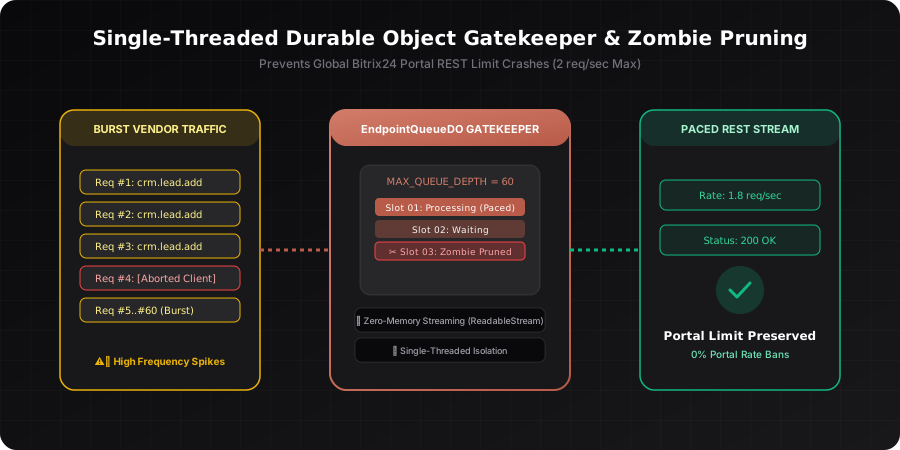
OIA Shield24 spins up single-threaded Durable Object queues per endpoint to enforce soft RPM throttling, featuring Zombie Request Pruning to protect global Bitrix24 limits.

Durable Objects Queue
04

Method & Scope Sandboxing

OIA Shield24 restricts vendors strictly to explicitly allowed Bitrix24 REST methods (e.g. crm.lead.add) and enforces allowed HTTP verbs (GET, POST, PUT, DELETE).

Scope Guard Plugin
05

CIDR IP & CORS Shield

Block rogue traffic at the edge. OIA Shield24 filters caller IPs against CIDR network allowlists and enforces origin domain restrictions before traffic touches Bitrix24.

WAF & Network Perimeter
06

Multi-Region Data Residency

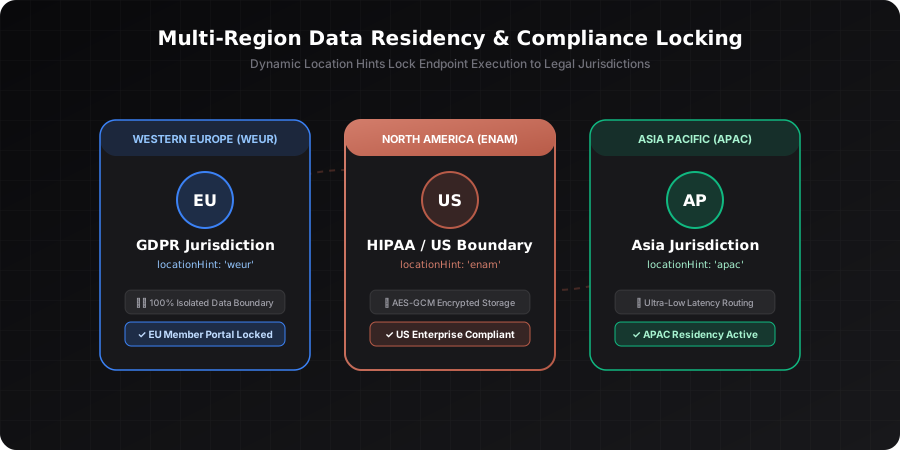
OIA Shield24 binds vendor endpoints strictly to Western Europe (weur), North America (enam), or Asia to satisfy GDPR, HIPAA, and regional laws.

Location Hints Locking
07

Member ID Alias Masking

OIA Shield24 masks your Bitrix24 portal Member ID using cryptographic alias routing, so a vendor's webhook URL never reveals your internal portal identity.

Alias ID Routing
08

Outbound Event Router

OIA Shield24 multiplexes Bitrix24 events to multiple external webhooks with exponential backoff retries via regional OutboundEventDO engines.
Alarm Retries Hub

Architected for Enterprise Governance.

Built on high-performance Edge Workers and Stateful Queue Engines, OIA Shield24 enforces per-endpoint rate limits, strict data payloads, and cryptographic verification at the edge.

Zero-Trust Cryptography

API keys are stored as deterministic SHA-256 hashes. Bitrix24 OAuth tokens are symmetrically encrypted via AES-GCM using Web Crypto API.

Absolute API Mimicry

Vendors can simply swap their Bitrix24 API URL to our OIA Shield24 edge proxy URL without altering their code. Payload responses pass through untouched.

Durable Rate Limiting

Our Durable Objects Gatekeeper acts as a single-threaded queue to enforce per-endpoint rate limits, preventing global Bitrix24 portal overload.

Visual Architecture Blueprint

How OIA Shield24 Governs Vendor Traffic

OIA Shield24 Zero-Trust Architecture Diagram
Security Deep Dive

Solving Bitrix24's Biggest Security Blindspot: Ungoverned Vendor Webhooks.

When enterprise teams hire third-party integrators, CRM agencies, or external marketing platforms, they are forced to hand over direct Bitrix24 webhooks or OAuth tokens. This grants complete, unmonitored read/write access to your entire portal's deal records, client databases, and financial data.

HIGH RISK: RAW B24 WEBHOOK
Direct Webhook Vulnerability
  • ✕ Full Portal Exposure: A single webhook key can read, modify, or permanently delete deals, leads, and contact databases.
  • ✕ Rate Limit Vulnerability: Rogue or buggy vendor scripts can crash your global Bitrix24 portal rate limits (2 REST calls/sec limit).
  • ✕ Zero Request Auditing: No IP whitelisting, no method filtering, and no visibility into stolen or leaked vendor tokens.
// Danger: Vendor can call destructive methods
POST /rest/1/raw_token/crm.deal.delete.json
Status: 200 OK (Entire Deal Deleted)
PROTECTED: OIA SHIELD24
OIA Shield24 Zero-Trust Perimeter
  • ✓ Method & Scope Sandboxing: Restrict vendor API access strictly to designated endpoints (e.g. `crm.lead.add` only).
  • ✓ Precision Payload Forcing: Deep JSON merging forces static company IDs or status codes into requests, blocking override attempts.
  • ✓ Durable Edge Throttle: Enforce strict per-vendor RPM caps with Zombie Request Pruning to protect portal health.
// Protected: OIA Shield24 Blocks Unauthorized Method
POST /handler/v_key/crm.deal.delete
Status: 403 Forbidden (OIA_ERROR_SCOPE_DENIED)
Field-Level Tamper Prevention

Deep JSON Payload Merging in Action

OIA Shield24 Precision Payload Forcing Diagram
Sub-10ms Edge Execution

The OIA Shield24 6-Stage Edge Middleware Cascade

Every incoming vendor request passes through a strict security assembly line before reaching Bitrix24.

STAGE 01

Analytics & SRE Telemetry

Wrapped in high-speed `try/finally` blocks. Tracks latency, execution region, HTTP codes, and payload sizes without blocking execution.

STAGE 02

SHA-256 Auth & On-the-Fly Token Refresh

Hashes proxy API keys for zero-trust lookup. Decrypts OAuth credentials using AES-GCM and refreshes expired B24 tokens automatically.

STAGE 03

Scope & IP CIDR Validation

Enforces exact HTTP Method rules, allowed origins (CORS), and checks caller IPs against strict CIDR network whitelists.

STAGE 04

Plan Quota & Tier Limiter

Evaluates endpoint usage against subscription tier limits (Starter, Developer, Enterprise) to prevent quota overruns.

STAGE 05

Zod WAF & Payload Forcing

Rejects payloads over 50MB. Performs deep JSON merges to inject forced parameters and sanitize malformed vendor input.

STAGE 06

Durable Object Gatekeeper

Dispatches request to a single-threaded Durable Object queue locked to your chosen legal region with zero-memory response streaming.

Portal Limit Protection Engine

Single-Threaded Durable Object Gatekeeper Mechanics

OIA Shield24 Durable Queue Pacer Diagram
Simple & Predictable Pricing

Choose Your OIA Shield24 Plan

Transparent subscription tiers designed to match your Bitrix24 portal scale and enterprise security requirements.

Starter Plan
Free / forever

Essential vendor governance for small Bitrix24 teams starting with basic proxy protection.

  • ✓ Up to 5 Active Proxy Endpoints
  • ✓ 60 Requests / Minute Soft Throttle
  • ✓ SHA-256 Key Hashing & AES Token Encryption
  • ✓ Basic REST Method Scope Restrictor
Install On Bitrix24
MOST POPULAR
Developer Plan
$10 / portal / month

Advanced payload forcing, CIDR IP filtering, and high-frequency rate pacing for growing businesses.

  • ✓ Up to 25 Active Proxy Endpoints
  • ✓ 300 Requests / Minute Rate Pacing
  • ✓ Precision Deep JSON Payload Forcing
  • ✓ CIDR Network Allow/Block Lists
  • ✓ 30-Day Threat Telemetry Logs
Install On Bitrix24
Enterprise Plan
$29 / portal / month

Multi-region jurisdictional compliance and dedicated Durable Object queues.

  • ✓ Unlimited Proxy Endpoints
  • ✓ Multi-Region Data Residency (EU, US, Asia)
  • ✓ Outbound Event Router Hub (OutboundEventDO)
  • ✓ 90-Day SRE Audit Telemetry & SLA
Install On Bitrix24

Not sure which plan fits your portal?

Talk to a Bitrix24 integration specialist about your specific vendor governance needs — no obligation.

Everything You Need to Know

Frequently Asked Questions

Got questions about how OIA Shield24 protects your Bitrix24 portal? Find detailed answers below.

1 How does OIA Shield24 protect my Bitrix24 portal from raw webhook leaks?

Direct Bitrix24 webhooks grant unrestricted access to your entire portal. OIA Shield24 acts as an edge proxy: vendors make calls to a unique OIA Shield24 URL using SHA-256 hashed keys. OIA Shield24 verifies scopes, IP allowlists, and rate limits before passing traffic to Bitrix24 over encrypted AES-GCM OAuth sessions.

2 What is Zero-Trust Cryptography and how are my OAuth tokens stored?

OIA Shield24 never stores plain-text API keys or raw OAuth tokens. All vendor proxy keys are saved strictly as SHA-256 hashes. Bitrix24 OAuth access and refresh tokens are encrypted at rest using AES-GCM Web Crypto and decrypted dynamically only in sub-10ms edge memory.

3 How does OIA Shield24 prevent my global Bitrix24 REST limits from crashing?

Bitrix24 enforces a global portal limit of 2 REST requests per second. OIA Shield24 spins up single-threaded Durable Object queues (`EndpointQueueDO`) for each proxy endpoint to pace vendor calls, buffer traffic spikes, and prune aborted zombie requests before they hit Bitrix24.

4 Can I restrict an external vendor to a single REST method like crm.lead.add?

Yes! OIA Shield24 features a strict Scope Guard Plugin. You can explicitly configure an endpoint to allow only `crm.lead.add` and restrict HTTP verbs to POST. If a vendor attempts to call `crm.deal.delete` or any unauthorized method, OIA Shield24 immediately blocks the request at the edge with a 403 status.

5 What is Precision Payload Forcing and how does it prevent parameter tampering?

Precision Payload Forcing automatically injects immutable fields (such as `ASSIGNED_BY_ID: 42` or a fixed Lead Source) into vendor JSON payloads. Even if a vendor script attempts to send a different user ID, OIA Shield24 overwrites the value using deep JSON merging before dispatching to Bitrix24.

6 How does Multi-Region Data Residency satisfy GDPR and HIPAA compliance?

With Jurisdictional Location Hints, OIA Shield24 locks stateful processing to designated jurisdictions—such as Western Europe (`weur`) for GDPR or North America (`enam`) for HIPAA. Payload data never leaves your chosen legal jurisdiction.

7 Does OIA Shield24 hide my real Bitrix24 portal URL from vendors?

Yes. Every webhook URL is built from a cryptographic Alias ID rather than your real Member ID, so a vendor never sees your internal Bitrix24 portal identity.

8 What happens if a vendor script sends malformed JSON or payloads over 50MB?

Our Zod WAF Validation Plugin checks incoming request structure and payload size at the edge. Requests exceeding 50MB or containing malformed JSON are immediately rejected with an `OIA_ERROR_PAYLOAD_TOO_LARGE` or `OIA_ERROR_INVALID_JSON` response without consuming Bitrix24 bandwidth.

9 Does OIA Shield24 handle automatic Bitrix24 OAuth token refreshes?

Yes! OIA Shield24 monitors OAuth token expiry during request authentication. If an access token has expired, OIA Shield24 seamlessly executes an on-the-fly token refresh with Bitrix24 servers and resumes the vendor request transparently.

10 How do I install OIA Shield24 on my Bitrix24 portal?

Installing OIA Shield24 takes less than 2 minutes. Simply click the "Install On Bitrix24" button to launch the official Bitrix24 Marketplace listing, authorize the application on your portal, and start creating secured vendor endpoints right away.

Enterprise Governance

Real-Time Observability & Jurisdictional Data Residency.

OIA Shield24 provides threat intelligence monitoring, health score metrics, and automated log evaporation. Keep your compliance officer happy with strict data residency controls.

🌐

Dynamic Location Hints

Bind vendor endpoints strictly to Western Europe (`weur`), North America (`enam`), or Asia to satisfy GDPR and HIPAA requirements.

📊

Threat Intelligence Engine

Real-time SRE metrics track unauthorized probes, brute-force API key attempts, and rate limit spikes. Logs automatically evaporate after 90 days.

oia-shield24-sre-audit.log
[13:42:01.002] INFO [OIA-Shield24-Analytics] Request ID: req_9x8f2a Region: WEUR
[13:42:01.004] INFO [OIA-Shield24-Auth] API Key Hash Verified (SHA-256) | Vendor: Agency_XYZ
[13:42:01.005] INFO [OIA-Shield24-Auth] B24 Token Valid (Decrypted AES-GCM)
[13:42:01.006] INFO [OIA-Shield24-Validation] Forced Overrides Applied: {"ASSIGNED_BY_ID": 42}
[13:42:01.008] INFO [OIA-Shield24-DurableObject] Dispatching to Queue (Queue Depth: 1)
✓ Response 200 OK (Latency: 7.2ms)
Jurisdictional Governance

Multi-Region Location Hints & Boundary Locking

OIA Shield24 Multi-Region Data Residency Diagram

Ready to Secure Your Bitrix24 Portal with OIA Shield24?

Join enterprise leaders using OIA Shield24 to isolate third-party vendors, eliminate unauthorized API access, and govern REST execution at the edge.